Graylog
Security Information and Event Mgmt. (SIEM)
Alternative Vendors


Commercial Alternatives


Key Features
Centralized Log Collection
Inputs for Syslog, GELF, Beats, Windows events, cloud services and more
Fast Search and Dashboards
Search across all logs, with saved searches, dashboards and widgets
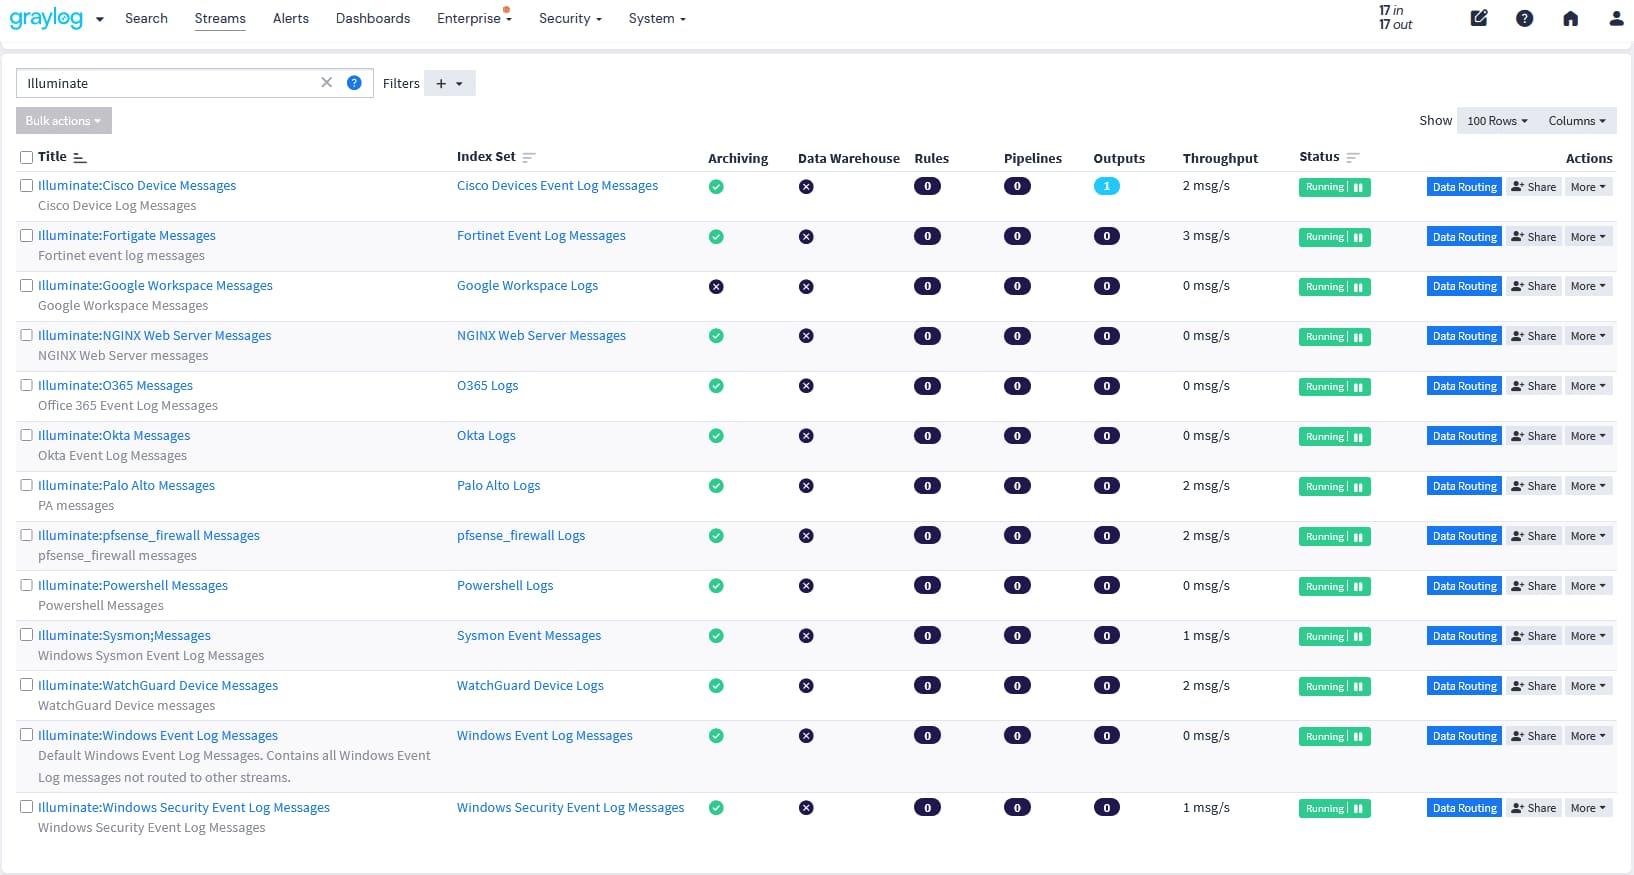
Streams and Pipelines
Route and transform messages in real time with stream rules and pipeline processing rules
Alerts and Event Definitions
Trigger notifications on conditions, aggregations or correlated events
SIEM (Graylog Security)
Detection rules, correlation, anomaly detection, investigations and MITRE ATT&CK mapping
Illuminate Content
Prebuilt parsing and normalization for common sources such as Windows, firewalls and Microsoft 365 (paid editions)
Pros and Cons
Pros
Free edition with no ingest cap
Graylog Open costs nothing and has no daily volume limit
Focused on logs
Simpler to run for log management than assembling a general-purpose stack
Powerful processing
Streams and pipeline rules route, enrich and filter data at ingest
Upgrade path to SIEM
Graylog Security adds detection and investigation on the same platform
Published starting prices
Enterprise and Security list starting annual prices
Cons
Not OSI open source
Graylog Open is source-available under SSPL, which restricts offering it as a service
Expensive jump to paid
Paid editions start at $15,000 to $18,000 per year
No true multi-tenancy
Separating MSP clients relies on streams, index sets and permissions
Infrastructure to manage
Self-managed installs need OpenSearch, MongoDB and capacity planning
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with Graylog.
Frequently Asked Questions
/vendor/graylog