Elastic Stack (ELK)
Security Information and Event Mgmt. (SIEM)
Alternative Vendors


Commercial Alternatives


Key Features
Elasticsearch
Distributed search and analytics engine for logs, metrics, traces and documents
Kibana
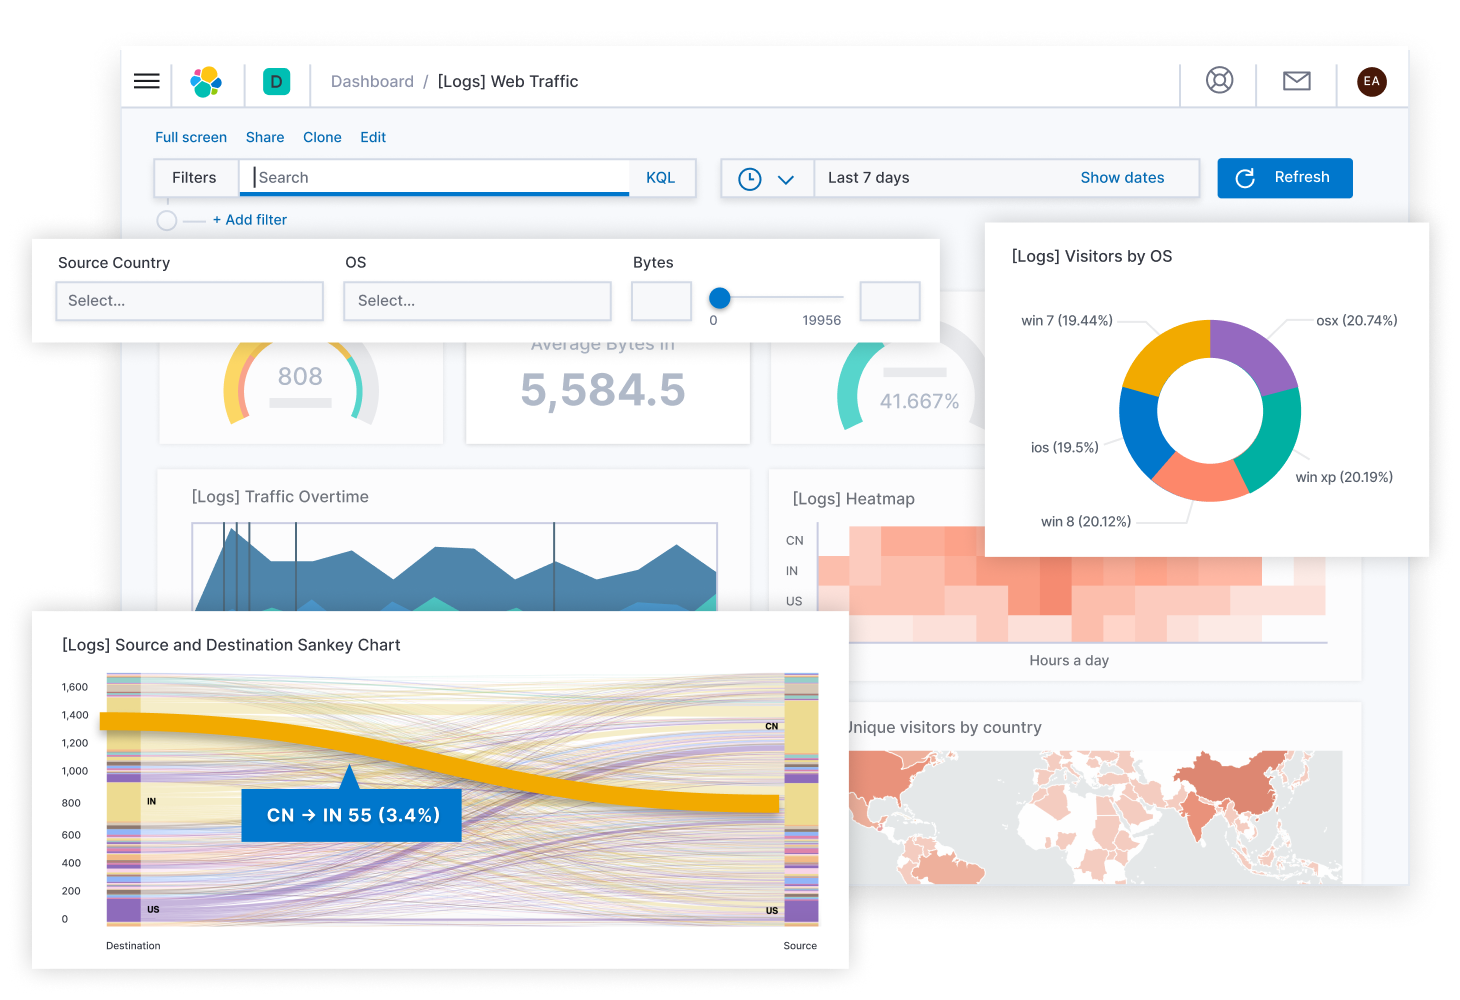
Dashboards, Discover search, alerting and management of the whole stack
Elastic Agent and Fleet
One agent for logs, metrics and endpoint security, centrally managed with Fleet; Beats remain for lightweight shipping
Logstash
Pipelines that ingest, parse and enrich data from many sources
Elastic Security
SIEM with detection rules, investigations and endpoint protection
Observability
Log, metric, APM and uptime monitoring in one interface
Pros and Cons
Pros
Open source again
Default code is available under AGPLv3 (alongside SSPL and Elastic License 2.0) since August 2024
Very flexible
One platform for log search, observability and SIEM
Scales horizontally
Clusters grow by adding nodes, with tiered storage for older data
Self-managed or cloud
Run it yourself for free or use Elastic Cloud Hosted or Serverless
Large ecosystem
Many integrations, client libraries and community resources
Cons
Key features are paid
SSO, machine learning, advanced detection and searchable snapshots need a subscription
Operational effort
Self-managed clusters need tuning, upgrades, index lifecycle and capacity planning
Resource hungry
Elasticsearch needs substantial memory and storage at scale, raising infrastructure cost
Licensing history
Past move away from open source and mixed licenses require care when building services on it
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with Elastic Stack (ELK).
Frequently Asked Questions
/vendor/elastic-stack