Microsoft Sentinel
Security Information and Event Mgmt. (SIEM)
Alternative Vendors


Commercial Alternatives


Key Features
Cloud-native SIEM
Fully managed on Azure with no servers to run; scales with ingested data.
Built-in SOAR playbooks
Automation rules and playbooks based on Azure Logic Apps run response actions across Microsoft and third-party tools.
Unified Defender portal
Sentinel incidents, hunting and Defender XDR alerts in one portal; the Azure portal experience retires after March 31, 2027.
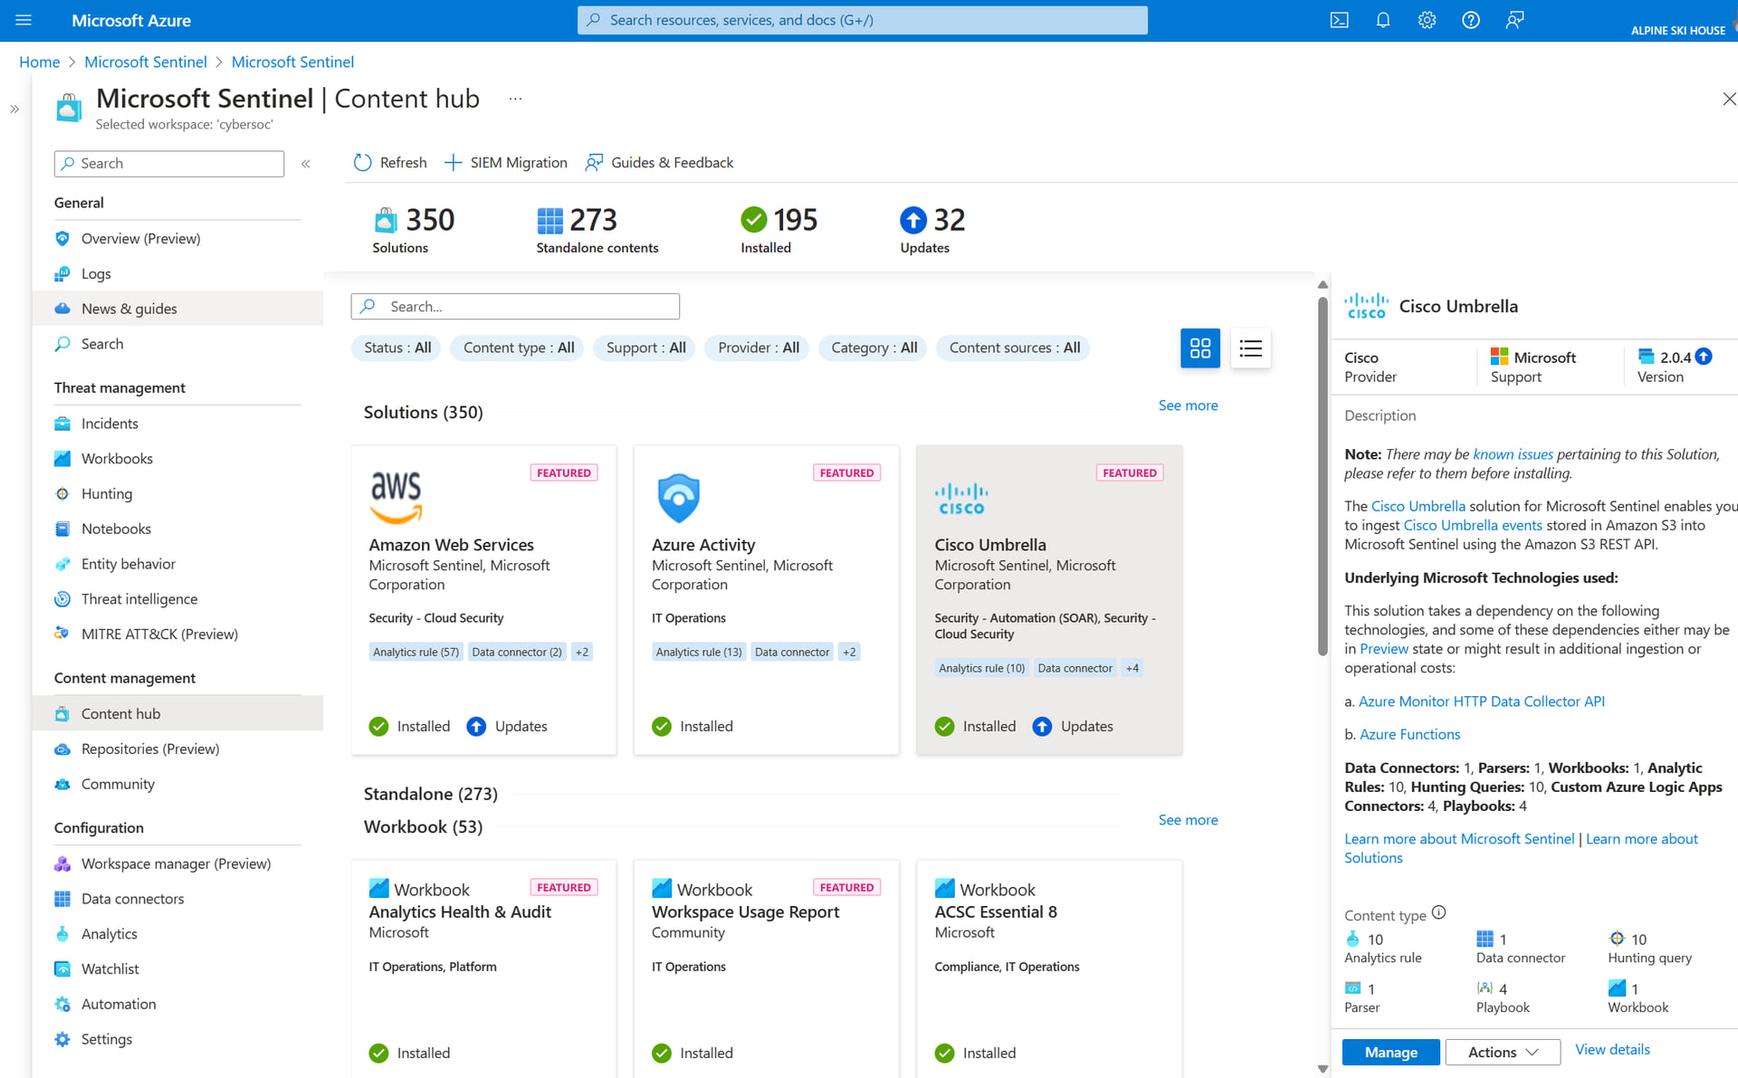
Data connectors and Content hub
Packaged solutions with connectors, analytics rules, workbooks and playbooks for Microsoft, cloud and third-party sources.
KQL threat hunting
Hunting queries, notebooks and analytics written in Kusto Query Language, with built-in hunting query libraries.
Sentinel data lake
Low-cost long-term storage tier for high-volume logs, queryable with KQL and notebooks.
Pros and Cons
Pros
Deep Microsoft integration
Native connectors for Microsoft 365, Entra ID, Defender and Azure, several of them free to ingest.
No infrastructure to run
Fully managed SaaS on Azure; scaling, patching and storage are handled by Microsoft.
MSP-friendly multi-tenancy
Azure Lighthouse and Defender multitenant management support managing many customer tenants.
Built-in automation
Logic Apps playbooks and automation rules are included without a separate SOAR product.
Tiered storage options
Data lake tier lowers the cost of keeping high-volume or long-retention logs.
Cons
Unpredictable consumption costs
Billing is per GB ingested, so noisy sources can drive costs up quickly without careful data filtering.
KQL learning curve
Effective rules, hunting and tuning require Kusto Query Language skills.
Azure-only, no self-hosting
Requires an Azure subscription and Log Analytics workspace; there is no on-premises option.
Portal migration work
Teams must move workflows to the Defender portal before the Azure portal experience retires in 2027.
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with Microsoft Sentinel.
Frequently Asked Questions
/vendor/microsoft-sentinel