Zeek
Network Management and Monitoring
Alternative Vendors


Commercial Alternatives


Key Features
Scripting Language
Event-driven language for writing custom detections, policies and log fields
File Extraction and Hashing
Identifies files transferred over the network, hashes them and can extract them for analysis
Spicy Parsers
Spicy parser generator for adding analyzers for new or proprietary protocols, including OT protocols
Package Manager
zkg installs community packages with extra analyzers, detections and log enrichments
Cluster Deployment
Scales across multiple worker processes and hosts to monitor high-bandwidth links
Intelligence Framework
Matches traffic against threat intelligence indicators loaded from files or feeds
Pros and Cons
Pros
Free and open source
BSD-style license with no cost or usage limits
Deep network visibility
Detailed, structured records of every connection and protocol transaction
Highly customizable
Scripting language and Spicy let teams write their own detections and parsers
SIEM friendly
JSON logs ingest cleanly into Elastic, Splunk, Sentinel and other SIEMs
Mature and actively developed
In development since the 1990s, with regular releases (9.0 in 2026)
Cons
No user interface
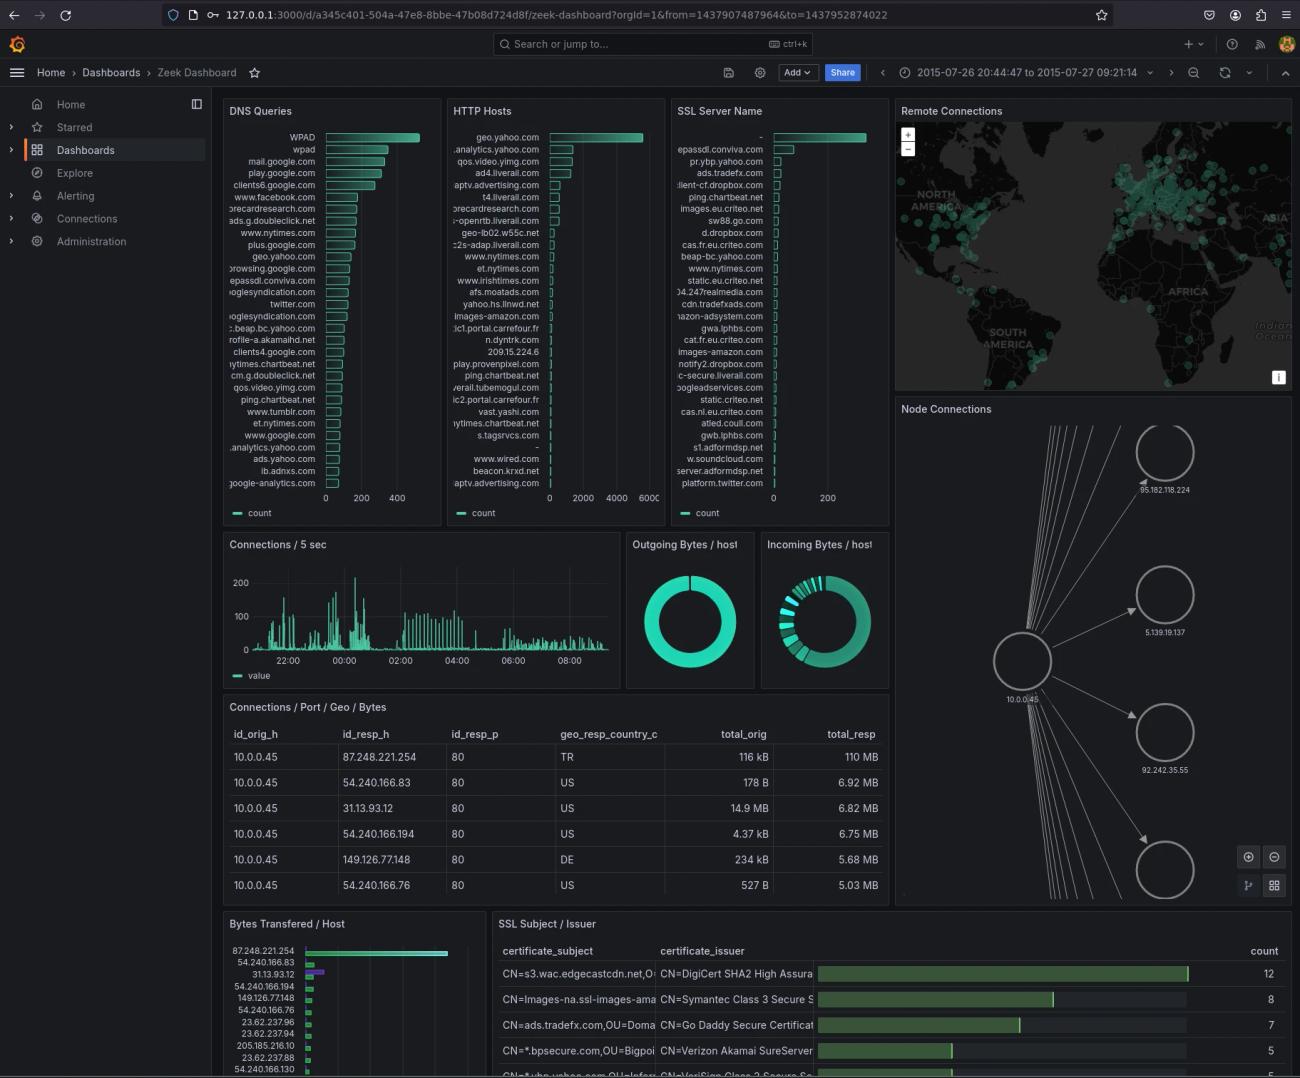
Command-line tool that produces logs; dashboards and search need a separate SIEM or log platform
Steep learning curve
Requires solid networking and scripting knowledge to deploy and tune
Needs network placement
A sensor must see traffic through a tap or span port at each site, which adds hardware and work for multi-client MSPs
Resource intensive at scale
High-bandwidth links need dedicated hardware and cluster configuration
No vendor support from the project
Support is community-based; commercial support comes through Corelight products
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with Zeek.
Frequently Asked Questions
/vendor/zeek