OpenEDR
Endpoint Detection and Response (EDR)
Alternative Vendors

Commercial Alternatives


Key Features
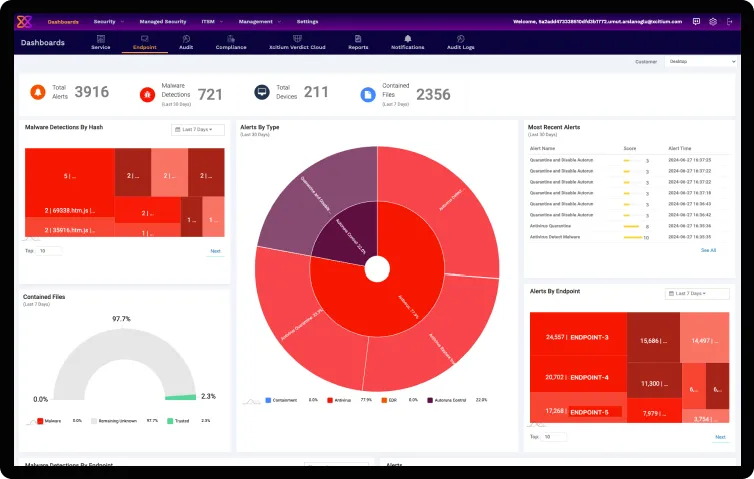
Endpoint Visibility
File and device trajectory, hashes, process hierarchy and per-event detail for each endpoint
Event Telemetry and Detection
Records base and advanced security events on the endpoint and raises detections mapped to MITRE ATT&CK
Response Actions (hosted platform)
Containment and response actions are available when the agent is managed from Xcitium's platform
Process Timeline and Tree
Process timeline, tree view and event search for root cause analysis
Kernel-Level Windows Monitoring
File-system mini-filter, process and registry callbacks, injected DLL API hooks and a network monitor on Windows
Hosted Console or Self-Built ELK
Use Xcitium's hosted platform, or send telemetry to your own Elasticsearch, Logstash and Kibana stack with the project guides
Pros and Cons
Pros
Zero Cost
No license fees for the EDR itself, per openedr.com
Detailed Telemetry
Process hierarchy, file trajectory and base-event telemetry for investigation
Source Code Available
Agent source is published on GitHub, so it can be audited and modified under the CASL terms
MSSP Use Allowed
The license explicitly lets MSSPs and SOCs build paid services on the software
Cons
Limited Commercial Support
Primarily community-driven support with limited commercial support options available
Self-Management Required
Requires in-house expertise for deployment, configuration, and ongoing maintenance
Smaller Community
Smaller user base compared to commercial EDR solutions, potentially limiting community resources
Integration Challenges
May require more effort to integrate with existing security infrastructure and SIEM systems
Source-Available, Not OSI Open Source
The Comodo Available Source License includes binding arbitration and other terms that differ from standard open source licenses
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with OpenEDR.
Frequently Asked Questions
/vendor/openedr