SentinelOne
Endpoint Detection and Response (EDR)
Alternative Vendors

Commercial Alternatives


Key Features
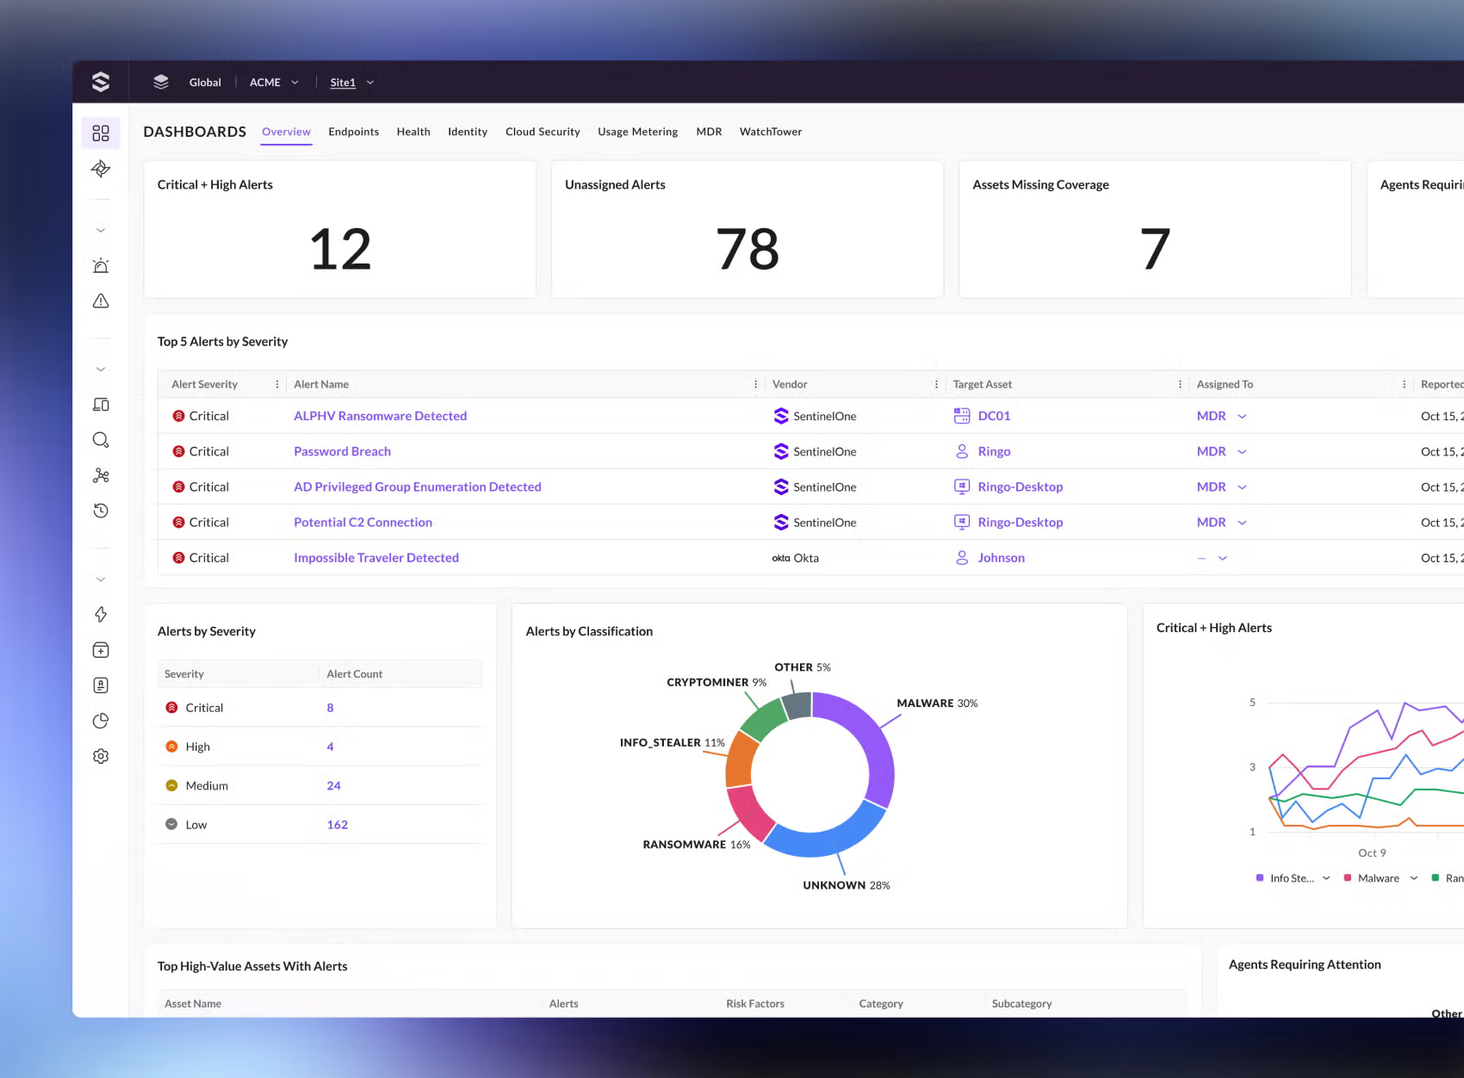
Autonomous threat response
The agent can kill, quarantine, isolate and remediate threats without waiting for an analyst.
Behavioral AI engine
Static and behavioural AI engines on the agent detect attacks in real time, including when the device is offline.
Remote shell access
Built-in remote shell gives PowerShell or bash access to an endpoint for investigation and remediation.
API-first platform
REST API covers platform functions for automation and integration with PSA, RMM and SIEM tools.
Storyline attack context
Automatically links related processes, files and network events into one storyline for each threat.
Ransomware rollback
One-click rollback on Windows restores files changed by ransomware using Volume Shadow Copy snapshots.
Pros and Cons
Pros
AI-powered detection
Behavioural AI on the agent detects attacks in real time, even offline.
Multi-tenant cloud console
Account, site and group hierarchy makes it practical to manage many clients from one console.
Autonomous response
The agent can contain and remediate threats automatically, reducing analyst workload.
Rollback functionality
One-click rollback reverses ransomware changes on Windows without reimaging.
Single agent
One agent covers EPP, EDR and cloud workloads.
Cons
Cost
Published packages start at $179.99 per endpoint per year, more than basic antivirus.
Advanced configuration
Policy, exclusion and site configuration has many options and takes time to tune.
No cheaper EPP-only package listed
The public price list no longer shows the entry Core and Control packages; the lowest listed package includes EDR.
Partner purchase only
Packages are bought through authorised partners, whose pricing takes precedence over the list price.
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with SentinelOne.
Frequently Asked Questions
/vendor/sentinelone