Huntress
Managed Detection and Response (MDR)
Alternative Vendors

Commercial Alternatives


Key Features
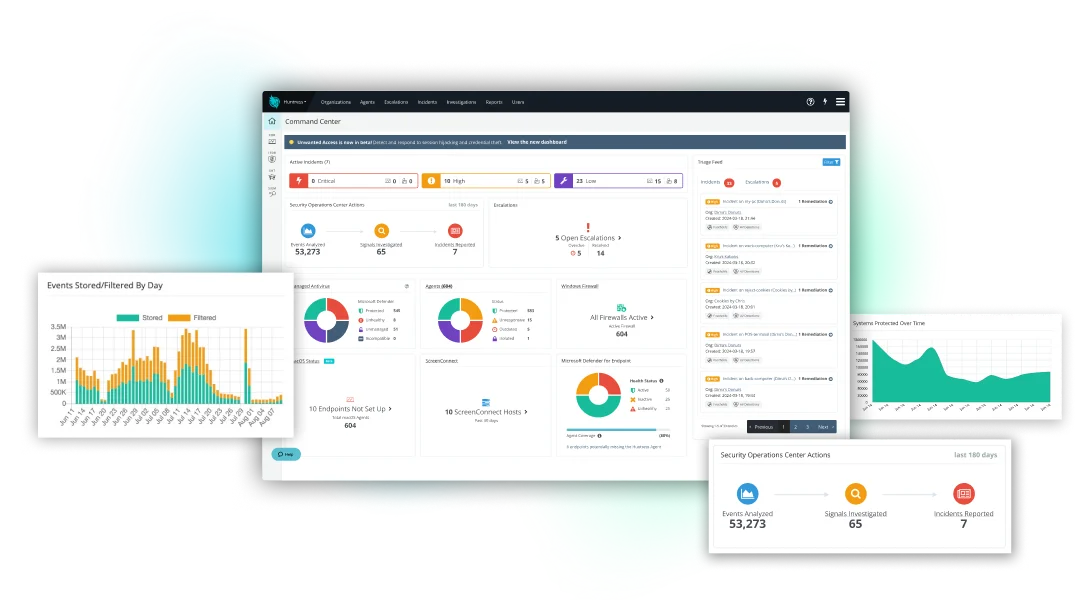
24/7 Security Operations Center
Huntress analysts review detections around the clock, write incident reports and carry out remediation steps
Managed EDR
Endpoint detection and response for Windows, macOS and Linux, including persistence and ransomware canary detection
Managed ITDR
Detects Microsoft 365 account takeover, session hijacking, suspicious inbox rules and risky sign-ins
Microsoft Defender Management
Manages the built-in Microsoft Defender Antivirus at no extra cost, or runs beside other antivirus products
Managed SIEM
Log collection with filtering at the source and SOC review, priced per data source
Security Posture Management
Managed ISPM and ESPM find identity and endpoint misconfigurations
Pros and Cons
Pros
Built for MSPs
Multi-tenant portal, no seat minimums through MSPs, monthly billing in arrears and free NFR licenses
SOC included
Every managed product is backed by the Huntress 24/7 SOC, with no separate SOC fee
Published per-unit pricing
List prices are on the website and fall with volume, so MSPs can model margins before talking to sales
Works with Microsoft Defender
Manages Defender Antivirus instead of requiring a separate antivirus license
Broad SMB coverage
EDR, identity, SIEM, posture and training from one vendor and one portal
Cons
Not built for large enterprises
Lighter feature set and fewer customization options than enterprise EDR and SIEM platforms
Cost adds up per product
Each product is priced separately per endpoint, identity, data source or learner
Seat minimums outside the MSP channel
Direct and reseller purchases require at least 50 seats per product
Cloud only
No self-hosted or on-premises option
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with Huntress.
Frequently Asked Questions
/vendor/huntress