ClamAV
Endpoint Security (Antivirus/EPP)
Alternative Vendors


Key Features
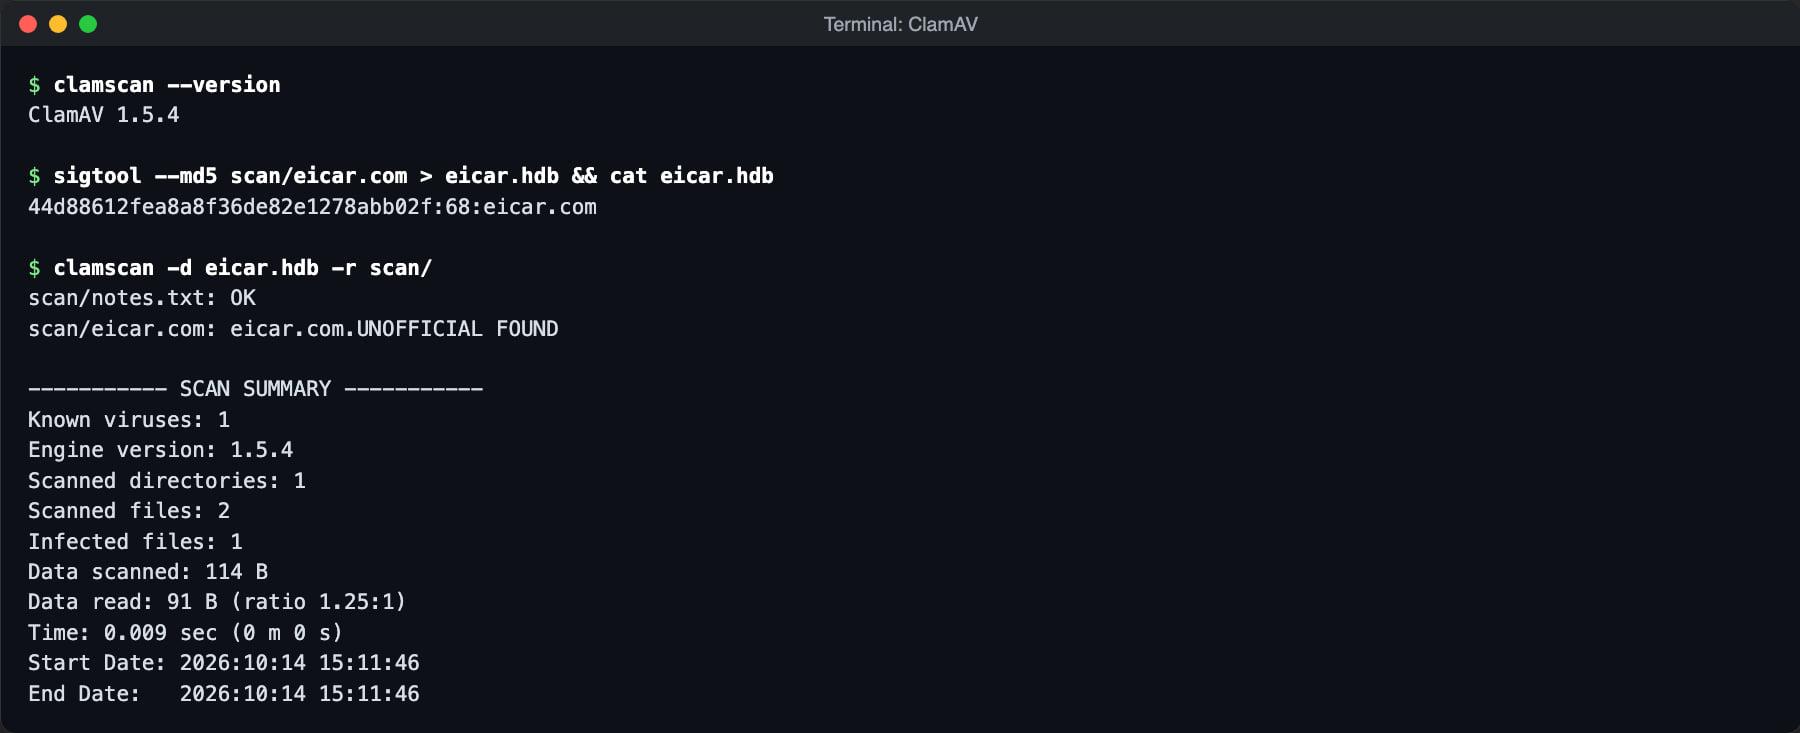
Custom signatures and YARA rules
Add your own hash, body and logical signatures or YARA rules alongside the official databases.
Long-term support releases
A designated LTS release line gets security fixes for longer, alongside the current feature release.
Mail gateway integration
clamav-milter and the clamd socket let Postfix, Sendmail, Exim and gateways such as Amavis, MailScanner and Proxmox Mail Gateway scan mail.
Automatic signature updates
freshclam downloads signature database updates from the ClamAV mirrors several times a day.
Wide file format support
Unpacks and scans archives (ZIP, RAR, 7z, TAR), Office documents, PDFs, executables and more.
Daemon and on-access scanning
The clamd daemon keeps signatures loaded for fast scans; clamonacc adds on-access scanning on Linux.
Pros and Cons
Pros
Completely Free and Open Source
Free under the GNU GPL v2 with full source code.
Lightweight and Efficient
Small footprint for command-line scans; the clamd daemon needs memory to hold the signature database.
Standard for mail servers
Supported by nearly every open-source mail gateway and MTA through clamd or clamav-milter.
Maintained by Cisco Talos
Cisco Talos maintains the engine and signatures, with regular releases on two supported lines.
Official Docker images
Ready-made clamav/clamav images make it easy to add scanning to upload and mail pipelines.
Cons
Command-Line Interface
Command-line tools only; graphical front-ends such as ClamTk are third-party projects.
Signature-based detection
Relies on signatures and heuristics, so it catches less new and targeted malware than commercial EDR products.
On-access scanning only on Linux
Real-time on-access scanning (clamonacc) is available only on Linux and needs extra setup.
No central management
No console, reporting or multi-tenant view; MSPs must monitor it through their RMM or SIEM.
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with ClamAV.
Frequently Asked Questions
/vendor/clamav