Tailscale
Zero Trust Network Access (ZTNA)


Commercial Alternatives


Key Features
WireGuard Mesh Network
Every device joins a private network (a tailnet) with a stable address. Connections run directly between devices over WireGuard, with encrypted relays only when NAT blocks a direct path.
Identity-Based Access Controls
Default-deny access rules written against users, groups and tags rather than IP ranges, so who can reach what follows the identity provider.
Sign-In Through Your Identity Provider
Google, Microsoft Entra ID, Okta, OneLogin, GitHub, Apple, passkeys or any custom OIDC provider. MFA is enforced by the provider you already run.
Subnet Routers and Exit Nodes
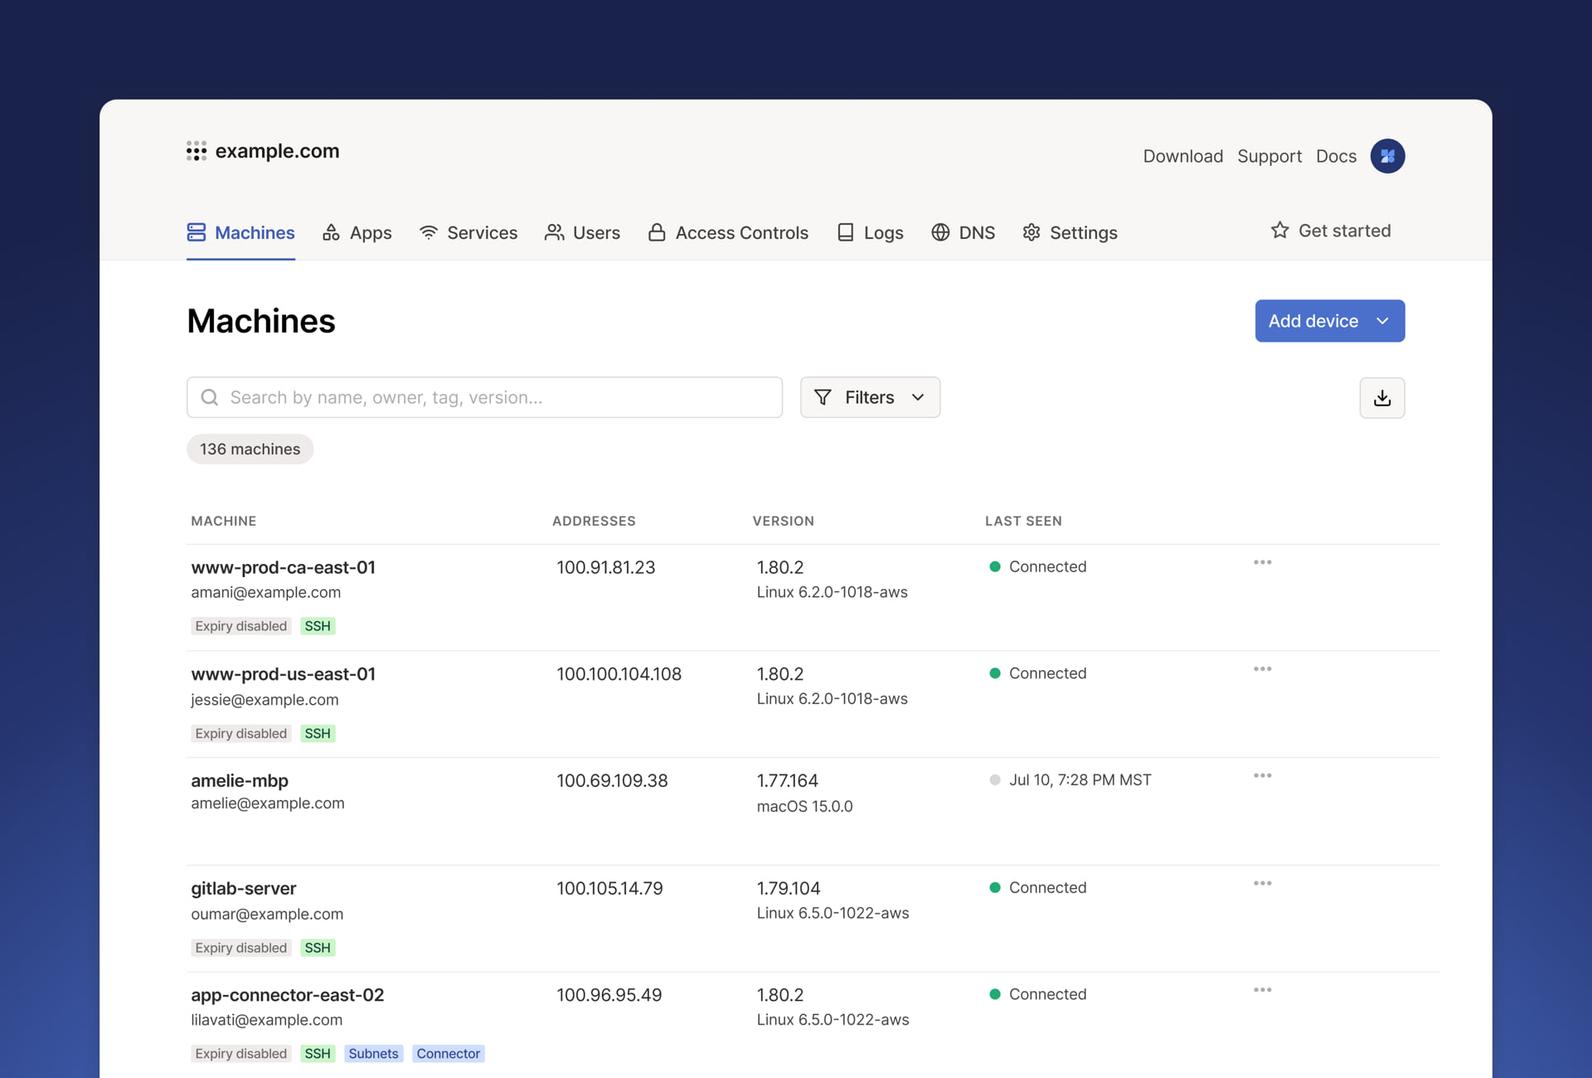
Reach whole networks and devices that cannot run the client (printers, NAS, legacy servers) through a subnet router, and route internet traffic through a chosen exit node.
Tailscale SSH
SSH to machines with access decided by the same access rules and identity, without managing SSH keys. Session recording is available on higher plans.
MagicDNS and HTTPS
Every device gets a name on the tailnet, and Tailscale can issue TLS certificates for internal services.
Pros and Cons
Pros
Setup in Minutes
Install the client, sign in with the identity provider, and devices are connected. No firewall ports to open and no VPN concentrator to run.
Direct, Fast Connections
Peer-to-peer WireGuard connections avoid hairpinning traffic through a central gateway.
Open Source Client
The client is BSD-3-Clause licensed, with over 37,000 GitHub stars and frequent releases.
Generous Free Plan
The Personal plan is free for up to 6 users with unlimited user devices, which suits labs and proofs of concept.
No Per-Device Charge for User Devices
Paid plans charge per user; user devices are unlimited on every plan.
Cons
Hosted Coordination Service
The coordination server is run by Tailscale. A self-hosted control plane is only available through the community Headscale project, which Tailscale does not support.
Per-User Pricing Adds Up
Standard is $8 and Premium $18 per user per month, which grows quickly for MSPs with many technicians and client users.
Advanced Features Gated to Premium
Just-in-time access, network flow logs, log streaming, regional routing and advanced SSH require the Premium or Enterprise plan.
Multi-Tenancy Through Sales
Running several tailnets, as an MSP with many clients would, is arranged through sales rather than self-service.
No Built-In Threat Detection
Tailscale secures connectivity; it does not inspect traffic for threats.
Feature Comparison
Comments
No reviews yet. Be the first to share your experience with Tailscale.
Frequently Asked Questions
vendor